Fractional Privacy Officer
Privacy leadership that turns requirements into operations.
Privacy expectations are rising quickly, and teams often struggle when regulations, customer requirements, and vendor reviews all start applying at once.
Cocoon CS Fractional Privacy Officer support gives you experienced guidance to build a privacy program that fits the business, from policies and notices to data workflows, vendor reviews, and privacy risk decisions.
What a Fractional Privacy Officer engagement is designed to solve
A fractional privacy leader helps organizations translate privacy expectations into day-to-day operating practice. The role defines governance, identifies how personal data moves through the organization, and puts practical controls in place that support regulatory and customer expectations.
How Cocoon CS operationalizes privacy leadership
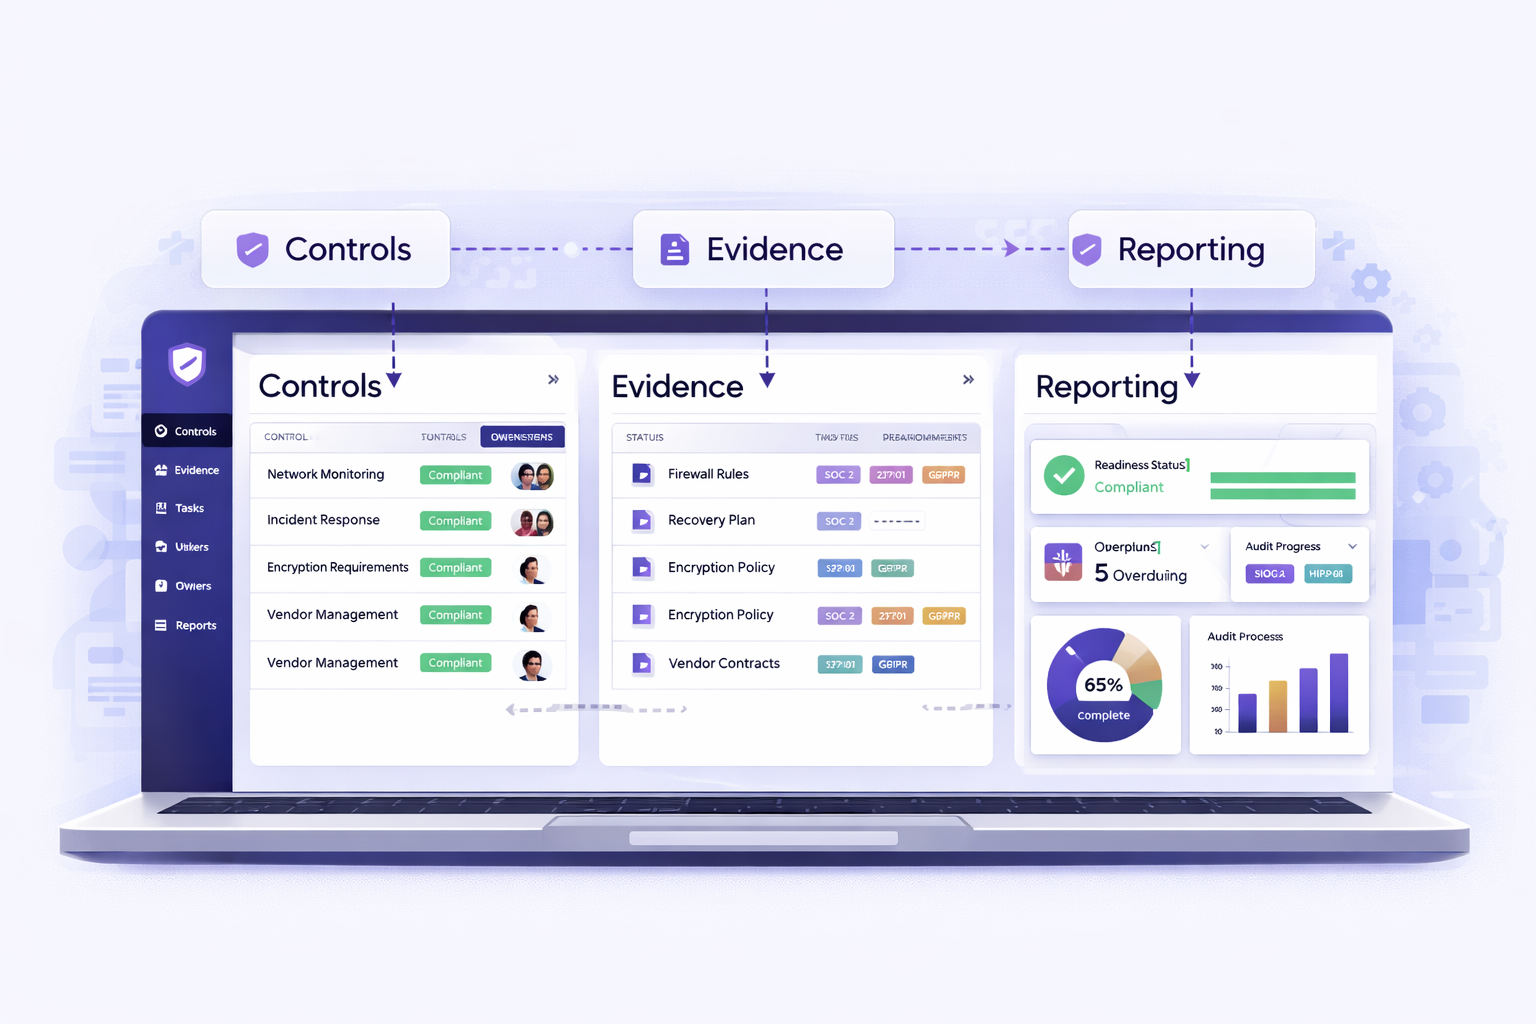
The role works best when privacy is treated as a program that touches product, operations, legal, security, and vendor relationships.
- Map the privacy landscape around data collection, processing, sharing, retention, and access.
- Define governance, policies, and workflows that fit the organization instead of creating unnecessary drag.
- Support privacy risk assessments, vendor reviews, and documentation for customer and regulatory scrutiny.
- Create a clearer operating cadence for access requests, retention decisions, incident escalation, and oversight.
Privacy made operational
Cocoon CS focuses on practical privacy delivery so the organization can improve risk control and transparency without slowing the business unnecessarily.
Business value and outcomes
Our Fractional Privacy Officer service helps organizations reduce privacy risk while improving clarity and readiness.

Build a pragmatic privacy program
Define governance, policies, and ownership that fit how the organization actually works.

Reduce privacy and regulatory risk
Identify high-risk processing and implement controls before issues become larger business problems.

Operationalize data workflows
Create repeatable processes for access requests, retention, and data handling decisions.
Common engagement areas
Typical engagements combine governance support with practical privacy operating work across the areas below.
Data mapping and records of processing
Clarify how personal data moves through systems, teams, vendors, and business processes.
Policy, notice, and consent updates
Refresh privacy-facing materials and internal guidance so they support real practices.
DPIAs, retention, and vendor privacy reviews
Strengthen privacy risk assessment, third-party diligence, and operational privacy controls.
Connect this service to the rest of your program
Use the service, platform, framework guidance, and industry context together so leadership support drives a broader operating model.
Questions teams usually ask about Fractional Privacy Officer support
Is this mainly for heavily regulated organizations?
No. Regulated organizations often need it, but growing companies also benefit when customer privacy reviews, vendor diligence, or expanding data use create operational pressure.
Does privacy leadership overlap with security and compliance work?
Yes. Privacy programs often work best when they are connected to the wider governance, risk, and evidence model instead of being managed in isolation.
Can this role help with customer and vendor privacy reviews?
Yes. That is a common part of the work, especially when privacy questions start appearing in procurement, contracts, or enterprise buyer diligence.